Scanners miss what attackers exploit
Automated scans list known flaws but miss logic errors and chained weaknesses. Manual testing shows what can really be reached and stolen.

Penetration testing · Antwerp
In Antwerp, we test your web applications, APIs, cloud and networks the way an attacker would. You get proven findings ranked by business risk, clear fixes and a retest to confirm they hold.
Local context
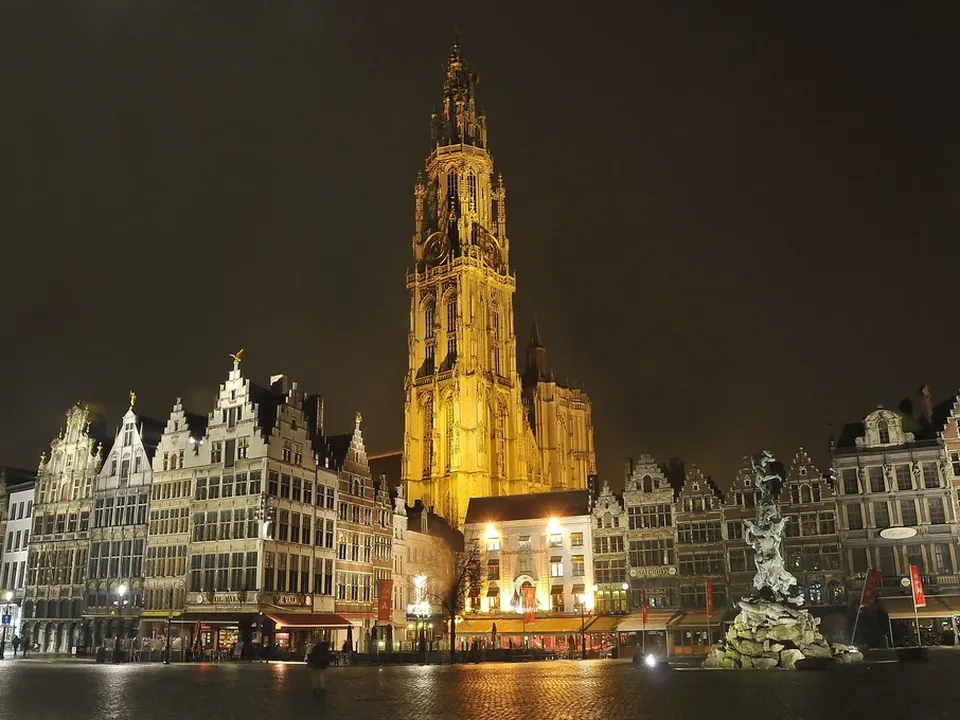
Antwerp supply chains run on data exchange: booking platforms, EDI flows, customs declarations and partner APIs. One weak API key or misconfigured portal can expose shipment data to the wrong party. We test these interfaces for authentication, access control and data exposure. Where partners connect to you, we check what they can reach beyond their own data.
Chemical plants raise a different concern: production networks must not be disrupted. We never scan control systems blindly. Instead, we test the boundary between office IT and operations, such as jump hosts, remote access and firewall rules. Any work closer to process equipment is agreed with your engineers, with test windows and stop rules in writing.
For trading houses, where email fraud is a common threat, it often makes sense to include Microsoft 365 and mailbox security. Internal tests take place at your premises or in the port area, about 45 minutes from our Brussels office by train. Reports are available in Dutch, English or French.
Antwerp is home to the Port of Antwerp-Bruges, one of Europe's largest ports, and to Europe's largest integrated chemical cluster. Logistics operators, chemical plants, diamond and trading houses depend on connected operational systems that suppliers and customers audit closely.
Antwerp is about 45 minutes from our Brussels office by train. We work on site at your premises or in the port area, or remotely.
What is at stake
Automated scans list known flaws but miss logic errors and chained weaknesses. Manual testing shows what can really be reached and stolen.
NIS 2, DORA and ISO 27001 all expect you to test the effectiveness of security measures. A test report is often the evidence auditors ask for.
Enterprise buyers and partners request a recent test before signing. An outdated or vague report raises more questions than it answers.
Key sectors in Antwerp
Tracking platforms and partner interfaces expose many entry points, and testing shows which ones lead to operations.
Testing the boundary between office and industrial networks shows whether an intrusion could reach process systems.
E-commerce sites and payment flows are prime targets, and testing them limits fraud and data theft.
Manufacturers learn from internal testing how far ransomware could spread from an office laptop to production.
What we do
We do not start everything at once. The scoping call shows which workstream matters most, and we start there.
We test authentication, access control, business logic and data exposure. The approach follows the OWASP testing guidance.
We probe your internet-facing perimeter and, from inside, test how far an attacker could move. Active Directory and segmentation are in scope when relevant.
We review cloud and identity settings for weaknesses that lead to data exposure or account takeover.
We choose the level of prior knowledge that matches your goal. Grey box often gives the best coverage for the time spent.
A 30-minute call is enough to define a test scope that matches your risks.
Regulators
Centre for Cybersecurity Belgium: national NIS 2 authority, registration and incident notification.
Belgian Data Protection Authority: GDPR supervision and complaints.
Financial supervisors for banks, insurers and investment firms, including DORA.
Belgian law of 26 April 2024, in force since 18 October 2024, with CyberFundamentals as the reference framework.
The method
Each step ends with a document you keep, even if the engagement stops.
A free 30-minute call to agree targets, test type and constraints.
Deliverable : Written scope and fixed price per lotWe fix test windows, contacts, exclusions and the legal authorisation to test.
Deliverable : Signed rules of engagementWe map the attack surface, then test manually with supporting tools.
Deliverable : Daily status notes and immediate alerts for critical findingsWe confirm each finding, remove false positives and rate impact on your business.
Deliverable : Findings list with severity and evidenceWe present the results to technical teams and to management separately.
Deliverable : Penetration test report with executive summaryOnce fixes are in place, we test again the findings you have corrected.
Deliverable : Retest report showing the status of each findingScope and budget
Questions
Yes, that is part of the rules of engagement. We set test windows, exclude fragile systems and agree a stop signal. Intrusive techniques on operational systems only happen with explicit approval from your engineers.
Yes. We write the report in English, Dutch or French, and the executive summary can also exist in a second language. Findings, ratings and evidence stay identical across versions.
We agree test windows and exclusions in advance. Risky actions are confirmed with you first. Production systems can be tested with care or replaced by a staging copy.
At least once a year is common practice. You should also test after major changes, such as a new application or a migration.
A scan is automated and lists known weaknesses. A penetration test is led by a person who confirms, chains and exploits weaknesses to show real impact.
Antwerp is about 45 minutes from our Brussels office by train. We work on site at your premises or in the port area, or remotely.
Last step
Tell us what you want tested and by when. You receive a written scope and a fixed price per lot after our call.