Clients and tenders require it
Large clients and public buyers increasingly ask for an ISO 27001 certificate before signing. Without one, security questionnaires slow down every deal.

ISO 27001 · Antwerp
In Antwerp, we build or align your information security management system with ISO/IEC 27001:2022, from gap analysis to the certification audit. You get an ISMS your teams can run and evidence an auditor can verify.
Local context
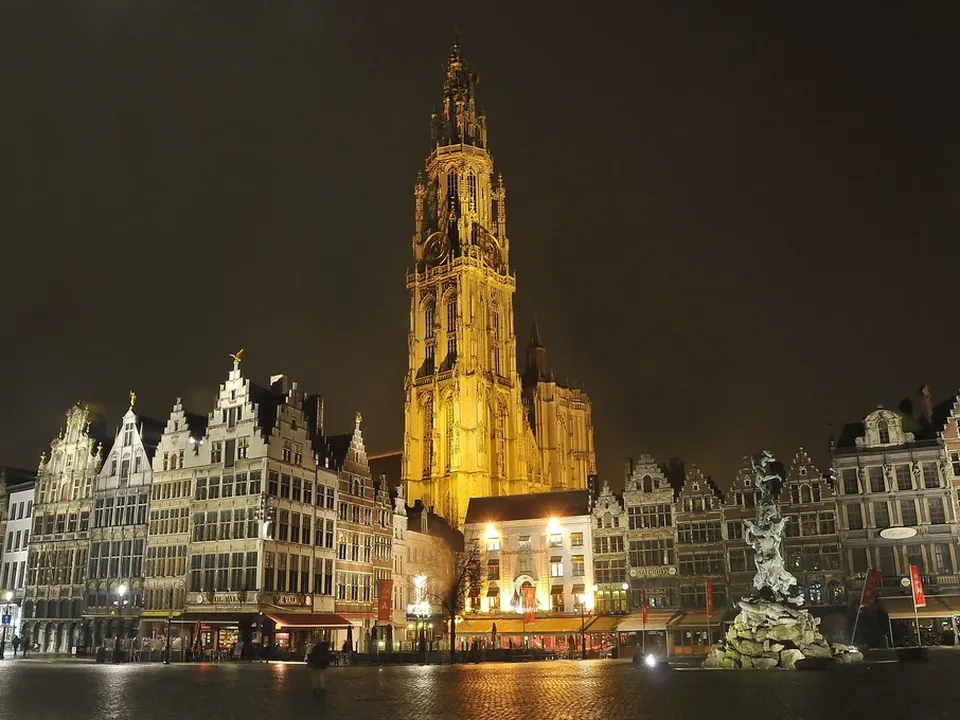
In Antwerp, customers rarely audit only your office network. Shippers, chemical groups and trading partners want to know how you protect booking data, cargo information and production systems. An ISO 27001 scope limited to corporate IT often fails that test. We help you decide whether terminals, warehouses or plant networks belong in scope, and what that implies.
Operational technology needs specific treatment in the risk assessment. A forwarder in the port area typically depends on shared port platforms, customs interfaces and carrier systems it does not control. We record these dependencies as supplier risks and choose the Annex A controls that fit them. For chemical sites, we align the ISMS with existing safety and process documentation.
Your teams usually work in Dutch, while group headquarters may expect English. We hold interviews in Dutch or English and keep the documentation in the language your auditors will use. Antwerp is about 45 minutes from our Brussels office by train. We plan on-site days at your premises or in the port area for interviews, walkthroughs and the internal audit.
Antwerp is home to the Port of Antwerp-Bruges, one of Europe's largest ports, and to Europe's largest integrated chemical cluster. Logistics operators, chemical plants, diamond and trading houses depend on connected operational systems that suppliers and customers audit closely.
Antwerp is about 45 minutes from our Brussels office by train. We work on site at your premises or in the port area, or remotely.
What is at stake
Large clients and public buyers increasingly ask for an ISO 27001 certificate before signing. Without one, security questionnaires slow down every deal.
The transition period from the 2013 version ended on 31 October 2025. Certificates based on the old Annex A are no longer valid.
Certification bodies raise nonconformities when risks, controls and evidence do not match. Major nonconformities must be closed before a certificate is issued.
Key sectors in Antwerp
Logistics firms exchange data with many partners, and a certificate shortens security reviews with shippers and carriers.
Chemical companies extend the ISMS to plant systems to protect formulas, safety data and process know-how.
Trading companies rely on ERP, payment and partner platforms, and an ISMS reduces fraud and disruption risks across them.
Manufacturers protect designs and production systems, and many large customers now require certification from their suppliers.
What we do
We do not start everything at once. The scoping call shows which workstream matters most, and we start there.
We define the ISMS scope, interested parties and boundaries, so the certificate covers what your clients actually buy.
We run a documented risk assessment and select controls from the 93 listed in Annex A. The result is your Statement of Applicability.
We write the required documented information and help your teams put controls in place. Everything stays proportionate to your size.
We organise an internal audit independent of the implementation work and prepare the management review. We then support you through Stage 1 and Stage 2.
Book a free 30-minute scoping call and get a written plan to reach certification.
Regulators
Centre for Cybersecurity Belgium: national NIS 2 authority, registration and incident notification.
Belgian Data Protection Authority: GDPR supervision and complaints.
Financial supervisors for banks, insurers and investment firms, including DORA.
Belgian law of 26 April 2024, in force since 18 October 2024, with CyberFundamentals as the reference framework.
The method
Each step ends with a document you keep, even if the engagement stops.
A free 30-minute call to understand your activities, systems and target date. We then send a written scope and a fixed price per lot.
Deliverable : Scope and fixed-price proposalWe compare your current practices with clauses 4 to 10 of the standard and with Annex A.
Deliverable : Gap analysis reportWe agree a risk method with you, identify and rate risks, and choose treatment options and controls.
Deliverable : Risk register and Statement of ApplicabilityWe draft policies and procedures and coach control owners until the controls run and produce evidence.
Deliverable : ISMS documentation setWe audit the ISMS against the standard and prepare the management review that must precede certification.
Deliverable : Internal audit report and management review minutesWe help you select an accredited certification body and support you through Stage 1 and Stage 2. We help close any findings.
Deliverable : Corrective action plan for audit findingsScope and budget
Questions
Include them if customers rely on them and you can manage them under the ISMS. A broader scope is more credible but takes more effort to run. We compare both options with you before the gap analysis.
It gives you a structured way to classify that information and control who receives it. Supplier and transfer controls in Annex A apply directly. Partners then get one consistent answer instead of ad hoc assurances.
No. Only an accredited certification body can issue an ISO 27001 certificate. We prepare you and support you during the audits, which keeps the certification independent.
The 2022 version groups Annex A into 93 controls across four themes and adds controls such as threat intelligence and cloud services. We run a targeted gap analysis and update your Statement of Applicability. Your certification body confirms which audit is required.
Yes. We work on site in Antwerp or remotely, in French, Dutch or English. You keep one named counterpart, and every step ends with a written deliverable you keep.
Antwerp is about 45 minutes from our Brussels office by train. We work on site at your premises or in the port area, or remotely.
Last step
Describe your scope and your target date. After a free 30-minute call, you receive a written scope and a fixed price per lot.