Management body accountability
NIS 2 requires the management body to approve cybersecurity risk measures and oversee their implementation. Its members must follow training and can be held liable for infringements.

NIS 2 compliance · Brussels
In Brussels, we help essential and important entities meet NIS 2, from scoping and gap analysis to incident reporting and board training. You end with a prioritised roadmap and documented evidence your management body can defend.
Local context
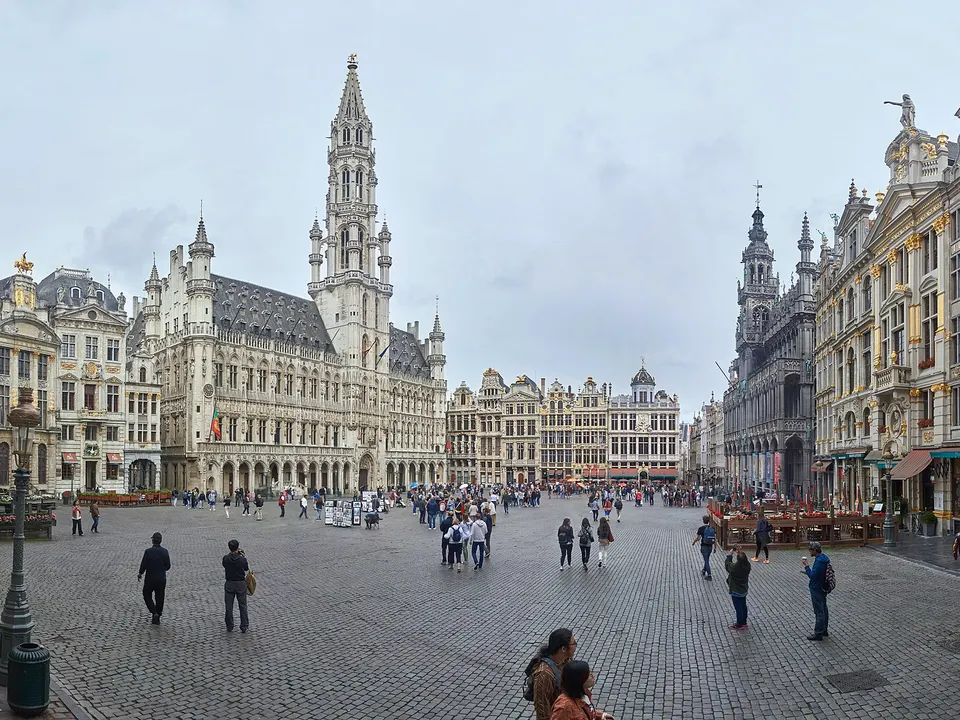
Brussels organisations often sit at the crossroads of several NIS 2 sectors. A federal administration, a group IT entity and a managed service provider can all fall in scope. Under the Belgian law of 26 April 2024, the CCB supervises them and receives their incident notifications. We first confirm your category and your registration duties with the CCB.
Many Brussels headquarters run security in French, Dutch and English at the same time. Policies, board briefings and incident playbooks must commit to exactly the same measures in each language. We draft them so that every version can be approved and defended. Banks and insurers mostly follow DORA under NBB or FSMA supervision, so we show where each regime applies across your group.
Our office is at Place Sainte-Gudule, so workshops with your management body can be arranged at short notice. We use CyberFundamentals, the Belgian reference framework, as the backbone of the gap analysis. You leave with a prioritised plan, director training and evidence the CCB or an assessor can check.
Brussels concentrates EU institutions, federal administrations, company headquarters, banks, insurers and law and consulting firms. Many organisations work in French, Dutch and English at the same time, and answer to both Belgian and European supervisors.
Our office is at Place Sainte-Gudule 14, in the city centre. We work on site in the 19 communes and the periphery, or remotely.
What is at stake
NIS 2 requires the management body to approve cybersecurity risk measures and oversee their implementation. Its members must follow training and can be held liable for infringements.
Significant incidents require an early warning within 24 hours, a notification within 72 hours and a final report within one month. Without a tested process, these deadlines slip.
Essential entities face fines up to €10 million or 2% of worldwide turnover. Important entities face up to €7 million or 1.4%, plus inspections and binding instructions.
Key sectors in Brussels
Public administrations are explicitly listed in NIS 2, so citizen-facing services need documented risk measures and a tested reporting process.
For banks and insurers DORA takes precedence, so we align NIS 2 work for group entities and ICT suppliers with DORA requirements.
Consulting and service firms are often outside direct scope but must meet NIS 2 requirements that clients impose by contract.
Cloud, data centre and managed service providers are in scope and are also asked for evidence by their own in-scope clients.
What we do
We do not start everything at once. The scoping call shows which workstream matters most, and we start there.
We check whether NIS 2 applies to you and in which category, based on sector, size and group structure. We also list your registration duties.
We assess your measures against the ten Article 21 areas, from risk analysis to access control and cryptography. Each gap is rated by risk and effort.
We design the detection, escalation and notification process, with templates for each reporting stage. We then test it in a tabletop exercise.
We set supplier security requirements, contract clauses and a review cycle. We prepare the approval, training and oversight routine of your management body.
Book a free 30-minute scoping call and get a written answer on scope and next steps.
Regulators
Centre for Cybersecurity Belgium: national NIS 2 authority, registration and incident notification.
Belgian Data Protection Authority: GDPR supervision and complaints.
Financial supervisors for banks, insurers and investment firms, including DORA.
Belgian law of 26 April 2024, in force since 18 October 2024, with CyberFundamentals as the reference framework.
The method
Each step ends with a document you keep, even if the engagement stops.
A free 30-minute call to understand your activities, size and group structure. We then send a written scope and a fixed price per lot.
Deliverable : Scope and fixed-price proposalWe confirm whether NIS 2 applies, which entity category you fall into and which obligations follow from the national transposition law.
Deliverable : Applicability memoInterviews, document review and sampling of technical controls against Article 21 and the applicable national framework.
Deliverable : Gap analysis report with risk ratingsWe sequence actions by risk, cost and deadline, and assign an owner to each one. Quick wins come first.
Deliverable : Prioritised remediation roadmapWe draft or update the policies, procedures and incident playbooks your teams will actually run.
Deliverable : Policy set and incident response playbookWe brief the management body, deliver its training and review progress at agreed intervals.
Deliverable : Board briefing pack and progress reportScope and budget
Questions
Most entities follow the law and authority of the country where they are established. Some digital providers are supervised where their main establishment sits. We map each entity to its authority and its registration duties.
Financial entities covered by DORA generally apply DORA rather than the NIS 2 risk and reporting rules. A subsidiary providing ICT services may sit on either side, depending on its role. We review your structure and document the answer for your supervisor.
It depends on your sector, your size and sometimes your role in a group. Medium and large companies in the listed sectors are generally in scope. Some entities are covered regardless of size. We confirm your position in a written applicability memo.
In-scope entities must manage the security risks of their suppliers. They pass requirements down through questionnaires and contract clauses. Being ready helps you answer quickly and keep those contracts.
Yes. We work on site in Brussels or remotely, as you prefer. Interviews and workshops run in French, Dutch or English, with one named counterpart throughout.
Last step
Tell us about your activities and your deadlines. After a free 30-minute call, you receive a written scope and a fixed price per lot.