Untested backups and single points of failure
Many firms discover during an incident that restores fail or one server carries everything. Downtime then hits revenue, contracts and staff at once.

IT infrastructure · Brussels
In Brussels, we design and deliver cloud, on-premise or hybrid infrastructure: identity, network, backup, Microsoft 365 and Azure. You get a documented system your teams control, with no black box.
Local context
Brussels organisations often run a head office, a few satellite sites and staff who switch between French, Dutch and English. Their infrastructure has to serve all of them without separate tools per team. We design identity, Microsoft 365 and network so that one set of rules covers every user and every site.
Many Brussels firms answer to more than one supervisor. A bank or insurer under NBB or FSMA oversight must show DORA evidence on backup, continuity and cloud providers. An entity covered by the Belgian NIS 2 law registers with the CCB and applies CyberFundamentals measures. We build the infrastructure so that this evidence comes out of daily operations.
Law and consulting firms in Brussels hold client files that the APD/GBA expects to be protected. For them, we focus on access rights, encrypted laptops and restores that are actually tested. Our office is at Place Sainte-Gudule, so on-site work in the 19 communes needs no travel planning.
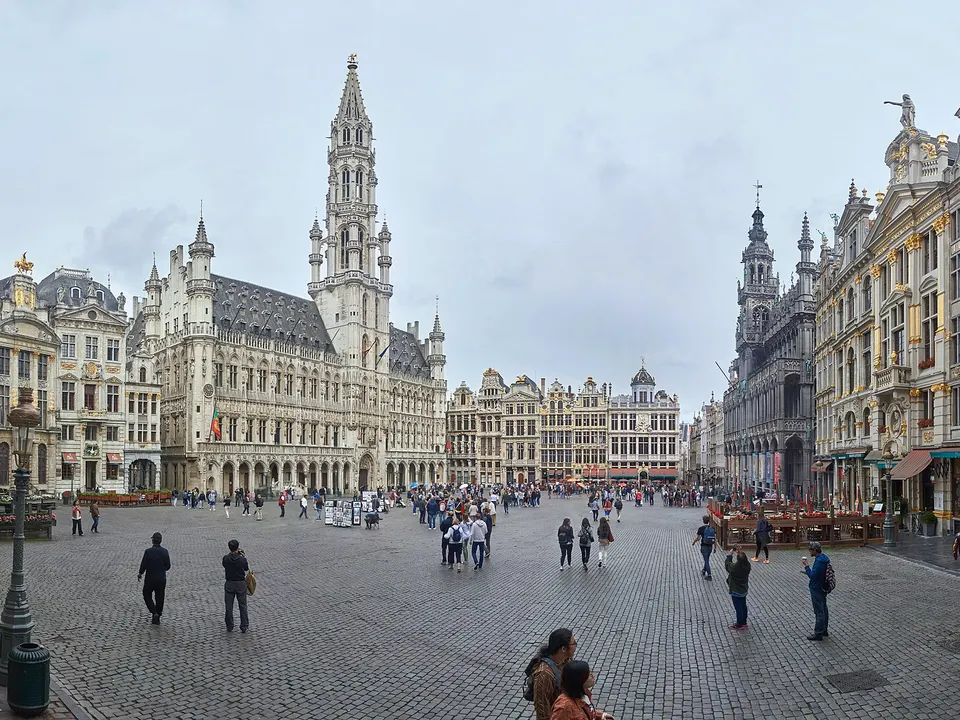
Brussels concentrates EU institutions, federal administrations, company headquarters, banks, insurers and law and consulting firms. Many organisations work in French, Dutch and English at the same time, and answer to both Belgian and European supervisors.
Our office is at Place Sainte-Gudule 14, in the city centre. We work on site in the 19 communes and the periphery, or remotely.
What is at stake
Many firms discover during an incident that restores fail or one server carries everything. Downtime then hits revenue, contracts and staff at once.
Shared admin accounts, missing MFA and stale users are the usual entry points of attacks. They also block any security audit or customer questionnaire.
NIS 2, DORA and ISO/IEC 27001:2022 expect evidence on access, backup, logging and continuity. Auditors ask for proof, not intentions.
Key sectors in Brussels
Public bodies need resilient, documented infrastructure that survives staff turnover and meets procurement and continuity rules.
Financial entities under DORA must prove ICT resilience, tested recovery and control over third-party providers.
Law, audit and consulting firms hold client files that require strong identity controls and reliable remote access.
Software firms need cloud foundations that scale, with clean identity and access that customers can audit.
What we do
We do not start everything at once. The scoping call shows which workstream matters most, and we start there.
We size the cloud, on-premise or hybrid target against capacity, resilience, run cost and dependencies. The design is one your teams and suppliers can execute.
We set up Entra ID, MFA, conditional access, admin tiers and Intune for endpoints. Accounts and rights become traceable and reviewable.
We segment the network, configure firewalls and remote access, and put backup under a tested restore routine. Recovery targets are written and checked.
We deliver the work ourselves, or we steer the integrator or MSP you want to keep. Either way, done criteria are agreed before work starts.
Book a free 30-minute call and we will tell you where the first risks sit.
Regulators
Centre for Cybersecurity Belgium: national NIS 2 authority, registration and incident notification.
Belgian Data Protection Authority: GDPR supervision and complaints.
Financial supervisors for banks, insurers and investment firms, including DORA.
Belgian law of 26 April 2024, in force since 18 October 2024, with CyberFundamentals as the reference framework.
The method
Each step ends with a document you keep, even if the engagement stops.
A free 30-minute call on sites, users, critical applications and continuity constraints. We confirm whether we are the right fit.
Deliverable : Scoping summaryWe map servers, cloud tenants, network, identities, backups and contracts. We note what is fragile and what is undocumented.
Deliverable : Infrastructure inventory and risk mapWe propose the target architecture with options, run cost and migration path. Each choice states its trade-off.
Deliverable : Target architecture documentWe cut the work into closed lots with price, timetable and done criteria. Nothing runs on open-ended time and materials.
Deliverable : Written scope and fixed price per lotWe build or supervise each lot: identity, network, backup, endpoints, cloud. Each lot ends with acceptance tests against the agreed criteria.
Deliverable : Acceptance report per lotWe hand over documentation, admin access, monitoring baseline and a tested restore. Your team or MSP can run the system without us.
Deliverable : Operations and recovery runbookScope and budget
Questions
Yes. Runbooks and architecture documents are written in the language your operations team uses. Admin settings stay in one language to avoid configuration errors. User guides can be prepared in French and Dutch.
DORA expects tested backup, documented recovery and control over ICT third parties, including cloud providers. We build those controls into the design and keep the test records. Your exchanges with the NBB or FSMA then rest on evidence rather than statements.
Both. Workshops, site surveys and cut-overs are often on-site in Brussels, and configuration work is mostly remote. We agree the split in the written scope.
Yes. We can steer your MSP or integrator and check their work against agreed criteria. You keep the provider relationship you value, with a clearer brief.
Not necessarily. Some workloads run better on-premise or in a hybrid set-up for cost, latency or data reasons. The target design compares the options with their run cost.
Last step
Tell us about your sites, users and critical applications. We reply with a written scope and a fixed price per lot.